emmtrix
Dependency
Analyzer (eDA)

Automatic Data Dependency and Signal Flow Analysis
emmtrix Dependency Analyzer (eDA) is an advanced tool that automates the static analysis of both legacy and AUTOSAR C code, with integrated support for analyzing the corresponding AUTOSAR model. It detects and visualizes data dependencies and signal flows by automatically analyzing how input variables influence output variables within the source code.
These input and output variables correspond to signals in AUTOSAR architectures or Simulink models and are crucial for demonstrating compliance with safety and emissions standards. This capability supports safety and reliability analyses of embedded applications and helps organizations meet regulatory requirements and industry standards.
Use Cases at a Glance:
Dependency Analysis of AUTOSAR Software Components

Figure 1: Typical AUTOSAR Workflow with Integrated eDA
Technical Workflow Details
Together with customers from automotive, we have implemented support for a use case so that our emmtrix Dependency Analyzer (eDA) can be used to extract and visualize the internal data dependencies and signal flows between AUTOSAR R-Ports and P-Ports of software components (SWCs) by analyzing their internal behavior.
A typical development flow in automotive is the usage of AUTOSAR to specify different software components and runnable entities. Simulink and Stateflow are used to implement the actual functionality and TargetLink is then used to generate the C code for the target platform. All data exchange in the application is typically modelled using AUTOSAR Runnables while the source code of the runtime environment is generated at the end when all components are integrated.
AUTOSAR Model and Code Analysis
eDA can be used to automatically analyze the generated C code regarding its data dependencies. The AUTOSAR model is used as a basis to generate analyzable code and the results of the source code analysis are mapped back to the data prototypes, variables and SWC ports as defined in the AUTOSAR model. This approach allows the verification that in the generated C code, all data dependencies are according to the model and no undesired connections exist between input and output ports of the model.
Designed for Automotive Scale
The tool was developed and is continuously enhanced in collaboration with automotive customers, including premium OEMs. It is designed to scale to ECUs comprising several million lines of code. To efficiently handle large codebases, individual runnables are analyzed separately, and the extracted dependencies and signal flows can later be merged for a complete system view.
Seamless Integration and Automation
Furthermore, it integrates seamlessly into CI pipelines to enable continuous analysis and comprehensive reporting.
Explore the Analysis Results
Results can be exported in exchange formats such as XML or JSON, or visualized in interactive graphical representations. The images below show example visualizations.
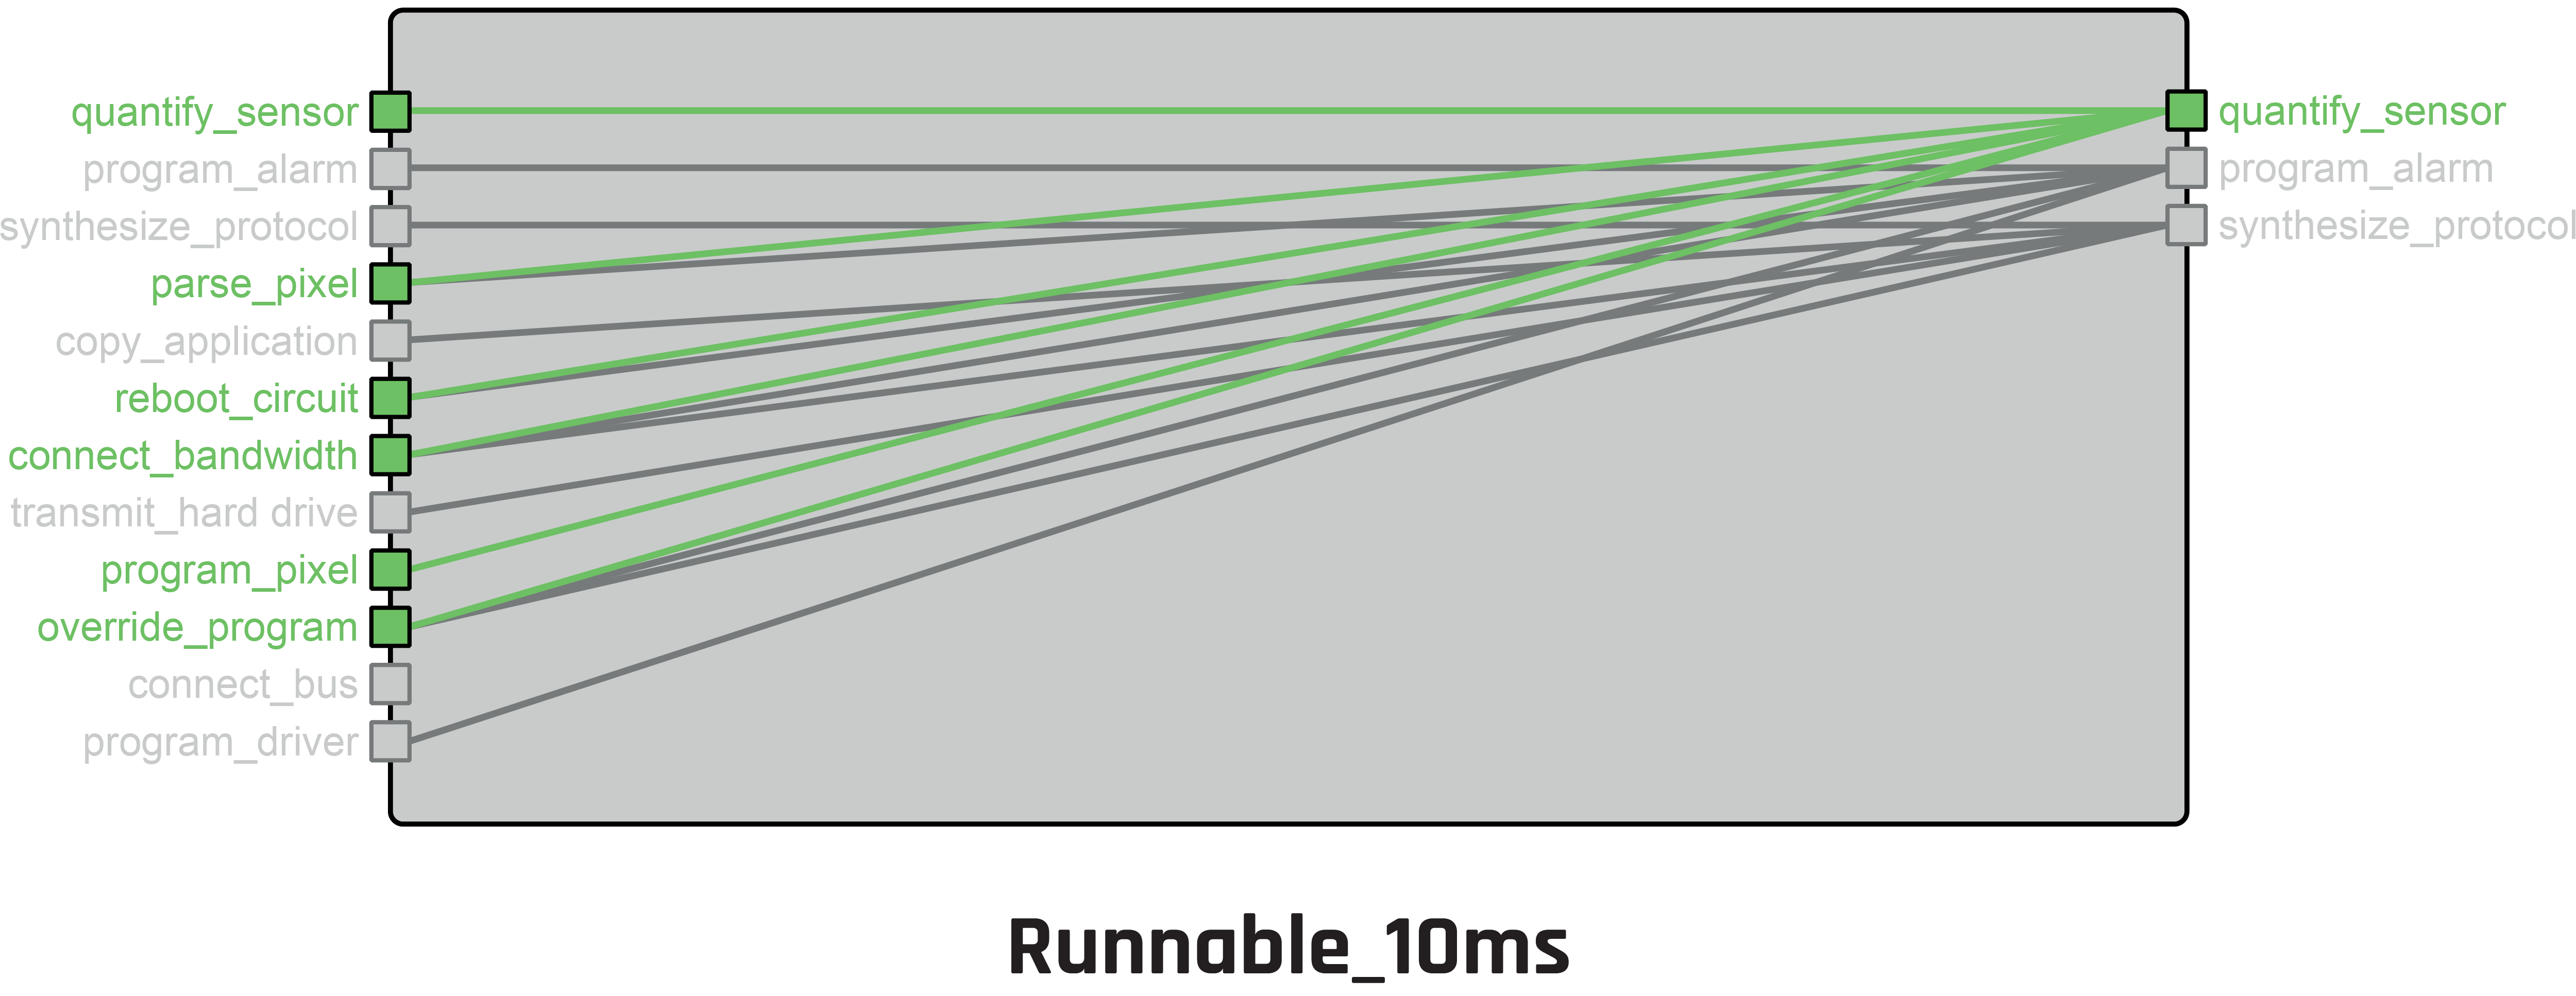
Figure 2: Internal Data Dependencies of a Runnable

Figure 3: Signal-Tracing across Subsystems
Key Features
Analysis Precision
- Advanced Static Analysis: Highly accurate and comprehensive dependency analysis with minimal false positives, based on advanced flow-, array-, field-, and call-sensitive techniques
- Validation: Proven in use — extensively validated in real-world automotive projects and through cross-validation across multiple analysis techniques
- Data and Control Dependencies: Signal-flow analysis with breakdown into data and control dependencies
Signals and Variants
- Stored Signals: Detection of stored signals across different runs (e.g. delay elements)
- Variant Handling: Supports analysis of software variants by ignoring dependencies in deactivated code, subsystems, etc.
- ECU Configuration: Consideration of internal ECU parameters (e.g. DCM, A2L)
Code and Model Mapping
- Supported Inputs: Supports analysis of plain C code, AUTOSAR C, and Simulink models including signal mappings and subsystem hierarchies
- RTE Generation: Automatic AUTOSAR Run-Time Environment (RTE) generation with signal mapping
- Model Transparency: Revealing internal model details of Simulink models (e.g. subsystems, signal and block names)
Scale and Reporting
- Large Codebases: Scales efficiently to projects with millions of lines of code through parallel processing and incremental analysis
- Reports and Traceability: Comprehensive reporting with reachability graphs, dependency matrices, and traceability reports for impact and safety analysis
- CI/CD Integration: Fully automated workflow with CI/CD integration
Key Benefits
- Verify Signal Connections: Ensure that there are no unwanted connections between input and output signals
- Track Signal Dependencies: Track down and document all modules affected by an input signal
- Minimize Re-Testing Effort: Identify which code will be affected by code changes to minimize re-testing effort
- Support Certification Documentation: Document all dependencies for any required certification process
Use Cases

Enhancing Emissions Compliance
In response to the 2015 emissions scandal, global regulatory bodies have significantly strengthened the requirements for vehicle emissions compliance and the integrity of On-Board Diagnostics (OBD) systems. Key authorities such as the Environmental Protection Agency (EPA) in the United States, the California Air Resources Board (CARB), and equivalent bodies in the European Union, under frameworks like the Euro Norms, are at the forefront of enforcing these enhanced regulations. Automobile manufacturers are now mandated to rigorously demonstrate that their vehicles, particularly the OBD software, are devoid of any manipulations and adhere to the prevailing emissions standards. This rigorous demonstration includes the submission of comprehensive documentation detailing the operation of their OBD systems. Such documentation must encompass thorough descriptions of the algorithms deployed for monitoring emissions, ensuring transparency and accountability. This step is crucial in rebuilding trust in automotive compliance and ensuring that vehicles on the road minimise emissions, aligning with initiatives like the Emission Neutral Default Action (ENDA) to mitigate any adverse environmental impacts.
The issue: Auto manufacturers face the challenge of ensuring their OBD software is fully compliant with stringent emission regulations. This entails not only adhering to legal requirements but also maintaining transparency and traceability in how the software manages and influences emissions. With regulatory scrutiny intensifying, manufacturers need a reliable method to analyze and document the behavior of their OBD systems under various conditions.
The solution: emmtrix Dependency Analyzer delves into the source code of OBD software, mapping out how specific input variables affect emission outputs. By identifying the intricate relationships between different components and variables, emmtrix Dependency Analyzer provides insight into the software’s operational logic.
Learn more
Our latest use case illustrates how the emmtrix Dependency Analyzer (eDA) uncovers hidden cross-domain dependencies — for example, how even a sunroof can directly impact OBD diagnostics and CARB compliance. This practical example demonstrates how eDA enables full transparency, reliable documentation, and compliance with strict regulations.

Freedom from Interference Analysis
In the development of safety-critical automotive software, ensuring the integrity and reliability of systems across varying levels of safety requirements is paramount. The emmtrix Dependency Analyzer offers a sophisticated solution to address the challenges associated with ensuring “Freedom from Interference” between components operating at different Automotive Safety Integrity Levels (ASILs). This use case outlines how the emmtrix Dependency Analyzer can be applied to identify and manage potential interference risks, thereby supporting compliance with ISO 26262 standards.
The issue: In modern automotive systems, software components with different safety requirements often share resources, such as CPUs, memory, or I/O systems. This shared environment raises the risk that lower-criticality components might interfere with the functioning of higher-criticality components, potentially leading to safety hazards. Ensuring freedom from interference is a regulatory requirement and critical for achieving functional safety certification under ISO 26262. However, manually identifying potential interference paths and ensuring isolation between components of different ASIL levels is both time-consuming and prone to human error.
The solution: emmtrix Dependency Analyzer automates the process of identifying and analyzing dependencies between software variables across different ASIL levels. By performing a comprehensive static code analysis, the tool maps out how each variable influences others, creating a detailed dependency graph that highlights potential interference risks between components of varying criticality.

Event Chain Analysis
In today’s complex software environments, understanding the dependencies and interactions between different parts of a system is critical. The emmtrix Dependency Analyzer is designed to address this challenge by providing deep insights into how variables within individual runnables influence each other across time. This use case explores the application of the emmtrix Dependency Analyzer for conducting an Event Chain Analysis, a method crucial for identifying and managing risks in software development projects.
The issue: In large-scale software projects, especially those involving real-time systems, it’s common to encounter issues related to timing, sequencing, and dependencies between tasks. Developers and project managers often struggle to trace how changes in one part of the system can affect others, potentially leading to unforeseen delays, bugs, or system failures. Without a detailed understanding of these dependencies, mitigating risks and ensuring system reliability becomes a shot in the dark.
The solution: emmtrix Dependency Analyzer offers a powerful solution by enabling users to perform a detailed analysis of dependencies within their software. By focusing on individual runnables, the tool can identify how changes in input variables affect output variables, including the detection of delay elements that indicate when a variable change will impact the system in the next time step. This capability is invaluable for constructing an accurate Event Chain Analysis, which is essential for risk identification and management.
Does one of these use cases sound familiar? Let’s talk about your specific scenario.
Technical Resources
Learn how emmtrix Dependency Analyzer processes dependencies, integrates with CI/CD pipelines and supports AUTOSAR workflows.
OBD Compliance Use Case
Explore how eDA supports dependency analysis for OBD compliance.
Tech Wiki
Explore technical documentation on eDA and dependency analysis.
Workflow Integration
Learn about integrating eDA into CI pipelines and AUTOSAR workflows.
Frequently Asked Questions
What types of code can eDA analyze?
eDA supports analysis of plain C code, AUTOSAR C, and Simulink models, including signal mappings and subsystem hierarchies.
How are analysis results mapped back to AUTOSAR?
The results of the source code analysis are mapped back to the data prototypes, variables, and SWC ports defined in the AUTOSAR model.
Which results and export formats are available?
eDA provides reachability graphs, dependency matrices, and traceability reports for impact and safety analysis. Results can be exported in exchange formats such as XML or JSON.
Can eDA analyze software variants?
Yes. eDA supports analysis of software variants by ignoring dependencies in deactivated code, subsystems, and other deactivated parts of the software.
Can dependency analysis run in a CI/CD pipeline?
Yes. eDA supports a fully automated workflow with CI/CD integration for continuous analysis and reporting.
Let’s Get in Touch
Would you like to understand the dependencies and signal flows in your embedded software? Contact us to discuss your C code, AUTOSAR environment, and analysis requirements, or request a demo.